 Risk Management and Vendor Oversight
Third-Party Risk Assessment Framework Selection for Compliance Programs
Match your obligations and vendor depth to layered frameworks.
Compliance Primer Editors·
 ISO 27001 and Multi-Framework Programs
Building a Unified Control Framework Across SOC 2 and ISO 27001
How to map one control library to both audits and cut duplicate work.
Compliance Primer Editors·
 ISO 27001 and Multi-Framework Programs
NIST 800-53 vs ISO 27001 Control Mapping Differences
Mapping these frameworks one-to-one hides gaps in both directions.
Compliance Primer Editors·
 SOC 2 Framework Mechanics
SOC 2 Bridge Letters and Gap Period Coverage
Management representations bridge SOC 2 audit gaps but require evidence to be credible.
Compliance Primer Editors·
 Audit Evidence and Fieldwork
Test of Controls vs Test of Details in Compliance Audits
Auditors must use both tests strategically, not interchangeably, to cover different risks.
Compliance Primer Editors·
 Audit Evidence and Fieldwork
Audit Risk Model Components for Compliance Practitioners
The model separates risk exposure from control strength to guide where audit effort matters most.
Compliance Primer Editors·
 Risk Management and Vendor Oversight
Vendor Risk Tiering for SOC 2 Subservice Organization Oversight
Subservice organization status depends on controls, not risk tier.
Compliance Primer Editors·
 Control Operation and Cadence
Security Awareness Training Completion Evidence for Compliance Audits
Compliance auditors now demand proof of behavioral change, not just training completion rates.
Compliance Primer Editors·
 Control Operation and Cadence
Patch Management Control Documentation for SOC 2 Audits
Auditors fail patch controls when documentation trails go missing, not patches themselves.
Compliance Primer Editors·
 Control Operation and Cadence
Incident Response Control Evidence Requirements for SOC 2
Auditors require three evidence layers to confirm incident response controls actually worked.
Compliance Primer Editors·
 Control Operation and Cadence
Designing an Access Review Program That Survives SOC 2 Sampling
Automate your access reviews to survive auditor sampling across the full compliance window.
Compliance Primer Editors·
 Control Operation and Cadence
SOC 2 Control Frequency Requirements by Control Type
Your written policies set the control frequency auditors will measure against.
Compliance Primer Editors·
 Control Operation and Cadence
Operationalizing a Control Calendar Across Multiple Compliance Frameworks
Unify compliance frameworks into one control calendar to eliminate duplicate auditing work.
Compliance Primer Editors·
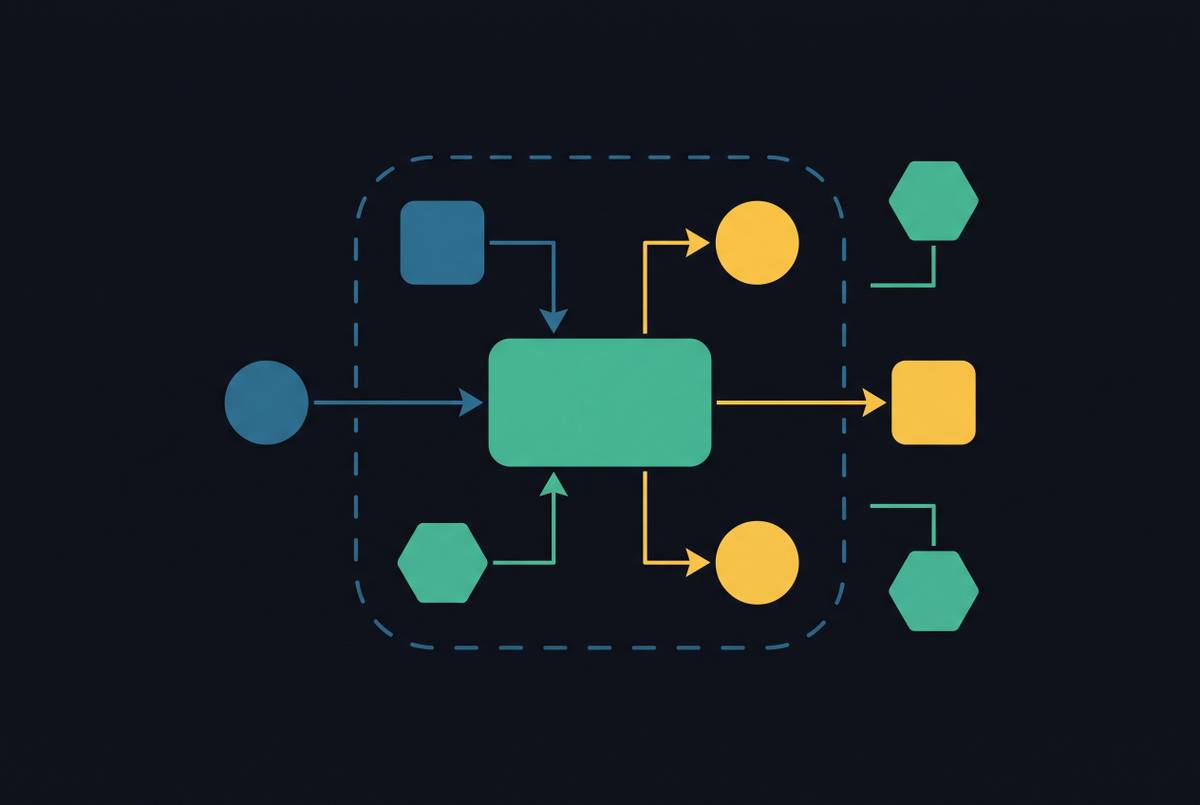 Scoping and System Boundaries
Third-Party Integrations and In-Scope Data Flow Decisions
Integrations pull third-party vendors into your compliance scope whether you notice or not.
Compliance Primer Editors·
 Scoping and System Boundaries
Scoping Physical Locations Into SOC 2 When the Company Is Fully Remote
Remote companies still have physical security scope, and it sits at the endpoint.
Compliance Primer Editors·
 Scoping and System Boundaries
Scoping Out Development Environments From SOC 2 Audits
Dev can stay out of scope only if three technical conditions hold.
Compliance Primer Editors·
 Scoping and System Boundaries
ISO 27001 Scope Statement Requirements and Boundary Documentation
Clause 4.3 inputs must be gathered first, then turned into boundary decisions.
Compliance Primer Editors·
 Scoping and System Boundaries
How Acquisitions and New Product Lines Affect SOC 2 Scope Mid-Cycle
Mid-cycle deals and launches force one of three scope paths.
Compliance Primer Editors·
 Features
Scoping Your System Boundary: What Is In and What Is Out
Where you draw the SOC 2 boundary shapes every audit that follows.
Compliance Primer Editors·
 Features
A Risk Assessment Methodology That Survives Fieldwork
How to build a risk register that survives an audit.
Compliance Primer Editors·
 Features
Access Reviews: Cadence, Scope, and the Paper Trail
How to set review cadence, attesters, and scope that survive audit.
Compliance Primer Editors·
 Features
Mapping SOC 2 Criteria to ISO 27001 Annex A Controls
Many SOC 2 controls carry over to ISO 27001, but risk methodology doesn't.
Compliance Primer Editors·
 Scoping and System Boundaries
People, Processes, and Technology Scope Components in SOC 2 System Descriptions
How DC3's five components decide what your SOC 2 audit covers.
Compliance Primer Editors·
 Scoping and System Boundaries
Defining the SOC 2 System Description Boundaries for a Multi-Tenant SaaS Product
How to decide which systems, vendors, and pipelines are in audit scope.
Compliance Primer Editors·
 ISO 27001 and Multi-Framework Programs
ISO 27001 Internal Audit Requirements and Practitioner Execution
A practical guide to Clause 9.2 audits that withstand certification scrutiny.
Compliance Primer Editors·
 ISO 27001 and Multi-Framework Programs
Running a Management Review Under ISO 27001 Requirements
Top management must actively lead the review, not delegate it to security staff.
Compliance Primer Editors·
 ISO 27001 and Multi-Framework Programs
ISO 27001 vs SOC 2 for US SaaS Companies Selling to Enterprise
Enterprise buyers demand SOC 2 in the US; international markets require ISO 27001 instead.
Compliance Primer Editors·
 ISO 27001 and Multi-Framework Programs
ISO 27001 Statement of Applicability Requirements and Common Mistakes
The SOA bridges your risk assessment to control implementation, and auditors scrutinize it first.
Compliance Primer Editors·
 ISO 27001 and Multi-Framework Programs
ISO 27001 Certification Audit Stage 1 vs Stage 2 Differences
Stage 1 confirms your security system exists on paper; Stage 2 proves it actually works.
Compliance Primer Editors·
 SOC 2 Framework Mechanics
SOC 2 Criteria Coverage for the Availability Trust Service Category
Three criteria govern system availability audits, and skipping their overlap breaks compliance.
Compliance Primer Editors·
 SOC 2 Framework Mechanics
Carve-Out vs Inclusive Subservice Organization Treatment in SOC 2
Misclassifying vendors at scoping remains the costliest mistake in SOC 2 audits.
Compliance Primer Editors·
 SOC 2 Framework Mechanics
Mapping Trust Service Criteria to Engineering Controls
Engineering teams must translate criteria into concrete controls to pass SOC 2 audits.
Compliance Primer Editors·
 SOC 2 Framework Mechanics
Common Controls Failures That Generate SOC 2 Exceptions
Five control failures drive nearly all SOC 2 exceptions, year after year.
Compliance Primer Editors·
 SOC 2 Framework Mechanics
SOC 2 Readiness Assessment vs Formal Gap Analysis
Readiness assessments define scope and prep systems before gaps can be meaningfully assessed.
Compliance Primer Editors·
 SOC 2 Framework Mechanics
Choosing a SOC 2 Auditor for a Series A SaaS Company
Type II demands the right auditor choice to avoid stalled enterprise deals and wasted runway.
Compliance Primer Editors·
 SOC 2 Framework Mechanics
SOC 2 Type I vs Type II for Cloud SaaS Vendors
Type II proves controls worked for months; Type I only shows they were designed right.
Compliance Primer Editors·
 Audit Evidence and Fieldwork
Managing Evidence for Automated Controls in CI/CD Pipelines
Automate evidence generation in your pipeline instead of scrambling before audits.
Compliance Primer Editors·
 Audit Evidence and Fieldwork
Auditor Sampling Methodology for SOC 2 Type II Controls
How auditors mathematically prove controls worked reliably across months, not just snapshots.
Compliance Primer Editors·
 Audit Evidence and Fieldwork
Continuous Evidence Collection vs Point-in-Time Sampling
Continuous monitoring catches compliance drift that annual snapshots miss until it's too late.
Compliance Primer Editors·
 Audit Evidence and Fieldwork
Screenshot Evidence Standards in SOC 2 Audits
Auditors reject screenshots missing timestamps, URLs, user IDs, or environment context.
Compliance Primer Editors·
 Audit Evidence and Fieldwork
Audit Findings vs Observations vs Exceptions in SOC 2 Reports
Three SOC 2 terms that sound alike mean entirely different things to auditors and buyers.
Compliance Primer Editors·
 Audit Evidence and Fieldwork
Observation Window Evidence Gaps and How Auditors Handle Them
Auditors bridge observation gaps with sampling and re-performance, not perfection.
Compliance Primer Editors·
 Audit Evidence and Fieldwork
Populating an Evidence Request List for SOC 2 Fieldwork
Learn what documents your auditor needs and how to organize them by control requirement.
Compliance Primer Editors·
 Audit Evidence and Fieldwork
Types of Audit Evidence Auditors Accept vs Reject
Sufficiency and appropriateness are the two tests that sort strong audit evidence from weak.
Compliance Primer Editors·
 Features
What Auditors Accept as Evidence, and What Gets Rejected
Auditors demand complete populations, system exports, and documented reasoning for every exclusion.
Compliance Primer Editors·
 Features
What a SOC 2 Type II Observation Window Actually Requires
The observation window determines how long your controls must run before an auditor can assess them.
Compliance Primer Editors·